Experience of successful fight against ransomware: practical guide
The experience of successfully combating ransomware shows: victory begins not on the day of the attack, but long before it. Companies that recover quickly from ransomware incidents know their critical systems in advance, have isolated backups, use MFA, segment the network, and regularly train their response teams. In this article, we will discuss how to act when infected, what helps to reduce damage, how to organize recovery, and which mistakes often turn a managed incident into a prolonged downtime.
Ransomware is malicious software that blocks access to data or systems and demands a ransom for decryption. Modern groups often operate on a double extortion scheme: first, they steal data, then they encrypt infrastructure and threaten publication. Therefore, fighting against ransomware is not only about antivirus solutions. It is a combination of technical measures, processes, legal readiness, and discipline within the company.
What is considered a successful fight against ransomware
Success does not always mean that the attack was completely prevented. In practice, a scenario is considered successful if the company:
- quickly detected suspicious activity;
- isolated infected nodes before widespread encryption;
- preserved evidence for investigation;
- restored critical services from clean backups;
- did not pay the ransom or depend on the perpetrator's promises;
- closed the initial attack vector;
- notified clients, partners, and regulators if required by law;
- improved security after the incident.
In other words, the goal is not to heroically "put out the fire," but to maintain business processes, minimize downtime, and prevent a repeat attack. Even if some data was encrypted, proper response can preserve reputation, funds, and manageability.
Why ransomware bypasses defenses
A common mistake is to assume that ransomware appears suddenly. In practice, an attack often develops in stages. First, intruders gain access, then establish footholds, escalate privileges, explore the network, disable protective measures, delete backups, and only then initiate encryption.
The most common entry points include:
- phishing emails with malicious attachments or links;
- stolen credentials for VPN, RDP, email, or cloud services;
- unprotected remote access;
- vulnerable public web applications;
- weak passwords and lack of multi-factor authentication;
- compromise of a contractor or supplier;
- outdated servers without security updates.
Thus, protection against ransomware should be built around the assumption that, at some point, the intruder will gain access. The question is how far they can advance and how quickly the team will notice.
The first minutes of the incident: step-by-step plan
At the moment ransomware is detected, the key is not to panic and improvise. A pre-approved response plan is necessary. Below is a practical sequence suitable for most organizations.
Step 1. Confirm the incident, but don’t waste time
Check for signs of the attack: mass file extension changes, ransom notes, sharp increases in write operations, disabling of antivirus, unusual administrator logins, unavailability of network folders. If signs match, act as if it’s a confirmed incident. Waiting for "full clarity" can give the ransomware additional hours.
Step 2. Isolate infected systems
Disconnect infected workstations and servers from the network. It’s better to sever the network connection than to immediately power off if there is a chance to preserve operational data for investigation. However, during active widespread encryption, a harsh shutdown may be acceptable to stop the spread.
Important: do not delete files, ransom notes, or logs. They may help identify the ransomware family, the attack pathway, and potential recovery keys.
Step 3. Stop the spread
Temporarily disable shared network resources, block suspicious accounts, force reset privileged user passwords, stop suspicious tasks in the scheduler, and block known indicators of compromise on firewalls, EDR, and proxies.
If the infrastructure is large, segment the response: first protect critical services, then office segments, and then the perimeter.
Step 4. Create a crisis team
The team should include IT, information security, management, legal, PR, the owner of critical business processes, and, if necessary, external incident response experts. One person should coordinate decisions. Otherwise, different teams might start restoring, erasing, and restarting systems without a comprehensive view.
Step 5. Document the facts
Keep a log of the incident: time of detection, affected nodes, actions taken by administrators, changes in rules, blocked accounts, communications with external parties. This log helps with investigations, insurance procedures, legal protection, and subsequent analysis of mistakes.
Step 6. Don’t rush recovery on top of infection
You cannot simply deploy a backup into a compromised environment. If the intruder has preserved access, they will re-encrypt the restored systems. First, you need to find and close the initial vector, check privileged accounts, clean the infrastructure, and only then restore services.
What does successful response look like in practice
Let’s consider a typical scenario without tying it to a specific company. An organization notices that the file server has started renaming documents, and users see ransom notes. The on-call administrator quickly disconnects the server from the network and reports to the response team. Meanwhile, the EDR shows suspicious logins from the account of a former contractor.
The team blocks the account, checks VPN logs, limits access between segments, and disables network folders. They then find that the contractor's account had not been revoked, and MFA was not applied for this user group. The file server backups were stored in a separate repository with immutable storage mode, so the intruders could not delete them.
Recovery starts with domain controllers and authentication systems, then file resources in an isolated segment are brought up, scanned, and access is gradually returned to users. The company loses part of the business day but does not pay the ransom and does not take weeks to recover.
Here, the key factors for success are simple: early detection, isolation, disabled unnecessary accounts, working backups, a clear recovery order, and no chaotic actions.
Backups as the main argument against paying ransom
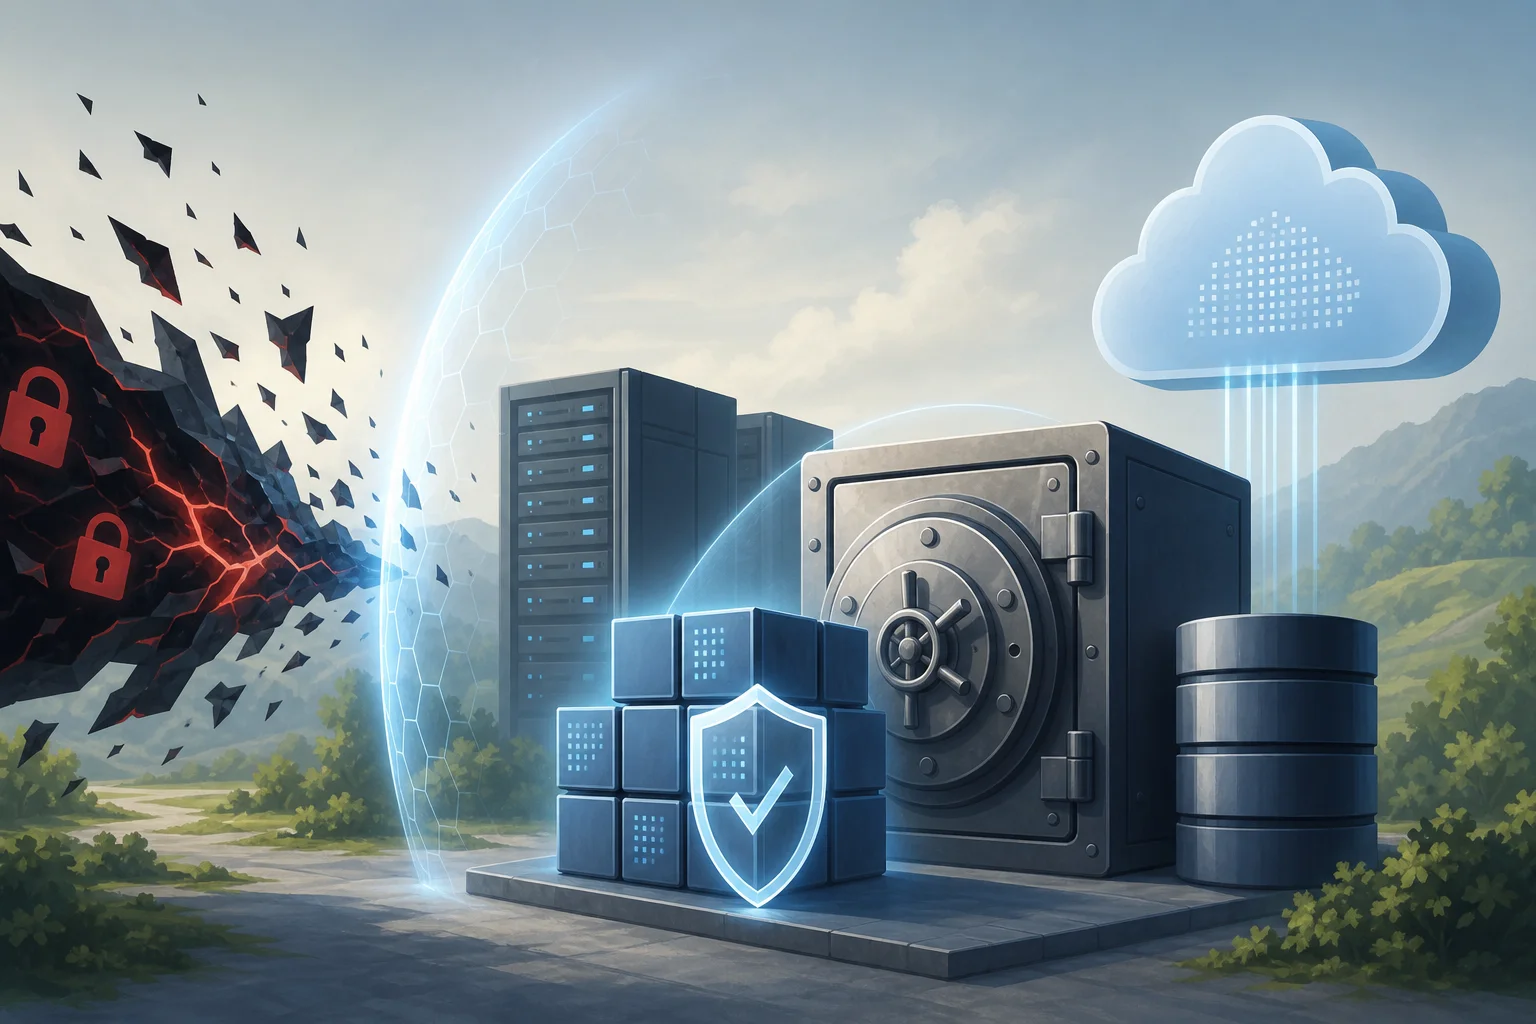
Backups are not a formality but the last line of defense. However, not every backup helps against ransomware. If copies are accessible from the same domain account, reside on a constantly connected network drive, or have not been checked for years, the intruders may encrypt them first.
A reliable strategy is based on the 3-2-1-1-0 principle:
- 3 copies of data: one primary and at least two backups;
- 2 different types of media or storage;
- 1 copy off-site;
- 1 immutable or offline copy;
- 0 errors during regular recovery checks.
What to check in the backup system
The minimum checklist looks like this:
- Are there separate accounts for managing backups?
- Is the backup console protected by MFA?
- Can copies be deleted from the domain in case of administrator compromises?
- Is there immutable storage, WORM mode, or offline media?
- Has recovery been tested in recent months?
- Is the recovery time known for critical systems?
- Are configurations for network equipment and protection measures saved?
- Is the recovery order for dependencies documented?
The last point is especially important. You cannot restore ERP if DNS, Active Directory, the database, licensing, and network routes are unavailable. Therefore, backup must be tied to the service map.
Table of security measures against ransomware
Below is a comparison of key measures. The table helps quickly understand which actions yield maximum effect and where weak points often emerge.
| Measure | What it provides | Common mistake | Priority |
|---|---|---|---|
| MFA for VPN, email, and administrators | Reduces the risk of login with stolen password | MFA only enabled for part of users | High |
| EDR or XDR | Detects suspicious behavior and lateral movement | Agents not installed on servers | High |
| Network segmentation | Limits the spread of the attack | All servers accessible from the office network | High |
| Isolated backups | Enable recovery without ransom | Copies accessible from the domain | Critical |
| Vulnerability management | Closes known entry points | Patches applied only on workstations | High |
| Principle of least privilege | Reduces damage from compromised accounts | Users accumulate unnecessary rights for years | High |
| Logs and SIEM | Helps investigate the attack | Logs retained for too short a time | Medium |
| Response drills | Accelerate decision-making during crises | There is a plan, but no one has tested it | High |
How to prepare infrastructure before an attack
Preparation is the cheapest stage of fighting ransomware. During an incident, each decision costs more: the business stops, data is unavailable, management demands timelines, and the team works under pressure.
Asset inventory
You cannot protect what you do not know. Create a list of servers, workstations, cloud resources, databases, network equipment, external services, and accounts. Distinguish critical systems: those which the business stops within hours without them.
For each asset, it is advisable to know the owner, criticality level, dependencies, location of backups, and acceptable downtime.
Access management
Ransomware often uses legitimate accounts. Therefore, access must be limited and verified. Remove accounts of former employees and contractors. Separate regular and administrative accounts. Enable MFA for remote access, email, cloud panels, and management systems.
It is also useful to implement PAM or at least temporary admin rights issuance. The fewer permanent privileges, the harder it is for an intruder to quickly seize the domain.
Segmentation and control of lateral movement
If one infected workstation sees all servers, the attack spreads quickly. Divide the network into zones: users, servers, administration, backups, production systems, guest networks. Allow only necessary connections.
Pay special attention to RDP, SMB, WinRM, SSH protocols, and remote administration tools. They are convenient for IT but also for attackers.
Email protection and user training
Phishing remains one of the frequent channels for initial access. Technical filters are needed, but they do not replace training. Users should understand what suspicious attachments look like, why they shouldn’t enter a password after clicking a link in an email, and who to report strange activity to.
Training works best when it is short, regular, and connected with real scenarios. It should not turn into a formal lecture once a year.
Recovery after an attack: the correct sequence
Recovery must be planned as a separate project. If services are brought up chaotically, valuable time may be lost, and the infrastructure might become infected again.
Recommended order:
- Determine the scope of the incident and the list of affected systems.
- Isolate a clean environment for recovery.
- Check backups for malware and signs of compromise.
- Restore core services: network, DNS, user directory, access management.
- Reset passwords and recreate key privileged accounts.
- Bring up critical business systems following a pre-approved priority.
- Conduct scanning and monitoring of restored nodes.
- Return users gradually, starting with the most important departments.
- Maintain enhanced monitoring for at least several weeks.
At the same time, it is important to separate two tasks: restoring operations and conducting investigations. They run in parallel but should not interfere with each other. For example, you cannot delete evidence on all servers for the sake of speed if part of the infrastructure is needed to determine the entry point.
Should you pay ransom to attackers?
In most cases, paying the ransom is not a reliable solution. There are several reasons. First, there is no guarantee that perpetrators will provide a working decryption key. Second, decrypting large volumes of data may take a long time and end in errors. Third, the fact of payment may make the company a target for future attacks. Fourth, there may be legal restrictions, especially if the payment recipient is linked to sanction lists.
However, the decision to negotiate is sometimes considered in crisis situations when lives, critical infrastructure, or the absence of backups are at stake. In such cases, one must not act alone. Lawyers, response experts, management, and legal risk assessment are needed.
Even if negotiations begin, the technical team must continue the investigation and recovery. The ransom does not close the security gap and does not eliminate the risk of data leaks.
Legal and communication actions
A ransomware incident almost always goes beyond IT. If personal data, trade secrets, or client data are affected, there may be obligations to notify regulators, partners, and data subjects. Specific requirements depend on jurisdiction, industry, and contracts.
Communications should be accurate and restrained. You should not state that “there is no leak” until the investigation is complete. It is better to use wording reflecting the facts: what has been discovered, what actions have been taken, which services are temporarily unavailable, when further updates will be provided.
Internally, a unified line is also needed. Users should know where to report suspicious emails, which systems should not be turned on, where to get current instructions, and who is answering customer questions.
Post-incident analysis
When services are restored, work does not end. Post-incident analysis helps turn a crisis into improved security. Analyze not only technical causes but also organizational ones.
Useful questions include:
- How did the intruders gain initial access?
- Why was the attack not detected earlier?
- What accounts and privileges were used?
- Which systems were encrypted and why?
- Did backups work?
- Which solutions took the most time?
- Were there communication issues?
- Which measures should be prioritized for implementation?
The outcome should be a plan for improvements with owners and deadlines. Without this, the organization risks experiencing a similar attack again.
Common mistakes in fighting ransomware
Even strong teams sometimes make mistakes under pressure. Here are the most dangerous ones.
Erasing systems without preserving evidence
If servers are reinstalled immediately, logs, malware files, autostart keys, and traces of the attackers’ movements can be lost. This complicates investigation and may leave the initial vector open.
Recovery in a compromised environment
If the domain, accounts, or administration tools are still under the attackers’ control, restored servers will be threatened again. The foundation must be cleaned first.
Blind faith in backups
A backup is considered operational only after successful test recovery. It’s necessary to check not only the presence of files but also the integrity of applications, databases, and dependencies.
Lack of an incident owner
When decisions are made by everyone at once, chaos ensues. A coordinator is needed who sees the comprehensive picture, sets priorities, and documents actions.
Silence about the problem
Attempting to cover up an incident can increase legal and reputational risks. It is better to prepare measured messages and update them as confirmed facts arise.
FAQ: common questions about fighting ransomware
Is it possible to decrypt files without paying ransom?
Sometimes yes. For certain old or incorrectly implemented families of ransomware, there are free decryptors. However, this is rare for modern attacks. Check the ransomware family through reputable specialists and public decryption projects, but do not rely solely on this option.
Should all computers be turned off immediately?
Not always. If encryption is spreading actively, isolation and shutdown may be justified. However, mass shutdown without a plan can destroy temporary investigation data. It is better to disconnect infected segments from the network and act according to the response plan.
Does antivirus help against ransomware?
Antivirus helps but is not complete protection. Modern attacks often use legitimate administration tools, stolen passwords, and manual actions by operators. Therefore, EDR, MFA, segmentation, privilege control, and backups are needed.
How often should recovery from backups be tested?
For critical systems — regularly, considering acceptable downtime. A good practice is to conduct scheduled tests several times a year and after major changes in the infrastructure. It is important to document actual recovery times and any issues encountered.
Can the risk of ransomware be completely eliminated?
The risk cannot be eliminated entirely. However, it can be significantly reduced, and damage can be limited. For this, layered protection, monitoring, a prepared team, and verified recovery are necessary.
Brief action plan for managers
If you need to quickly assess the company's readiness, start with ten questions:
- Is there a list of critical services and their acceptable downtime?
- Is MFA enabled for remote access and administrators?
- Are backups stored in an isolated or immutable form?
- Have recovery tests been conducted?
- Is there a response plan for ransomware?
- Is there a leader assigned to the crisis team?
- Is the network segmented?
- Are privileged accounts controlled?
- Are logs collected from critical systems?
- Have exercises been conducted in the past year?
If the answer to several questions is negative, that’s not a reason to panic. This is a roadmap. Start with MFA, backups, limiting privileges, and a response plan. These measures often have the fastest impact.
Conclusion
The experience of successfully combating ransomware boils down to readiness, discipline, and verified recovery. Don’t wait for an attack to find out where backups are, who makes decisions, and which servers are critical. Conduct an inventory, enable MFA, isolate backups, limit privileges, set up monitoring, and practice ransomware scenarios in drills. The earlier you start, the greater the chance to stop an attack without paying ransom and quickly return to business.